Anticipate risk. Strengthen defense. Prepare to respond.
Governance and compliance, penetration testing, detection and incident response: one coherent program, sized for your organization and your obligations.
Discuss this needThree areas, one program.
Start with an assessment or choose a focused engagement.
Governance & compliance
Set the direction: maturity, risk, policies, data-protection compliance and program oversight.
- Maturity assessment and roadmap
- Data-protection (CDP) compliance and audit readiness
- Fractional CISO
- Staff awareness
Penetration testing & Red Team
Test your defenses within an authorized engagement, then verify the fixes.
- Web, mobile and network penetration testing
- Cloud and Microsoft 365 configuration review
- Agreed Red Team exercises
- Retest after remediation
Detection & response
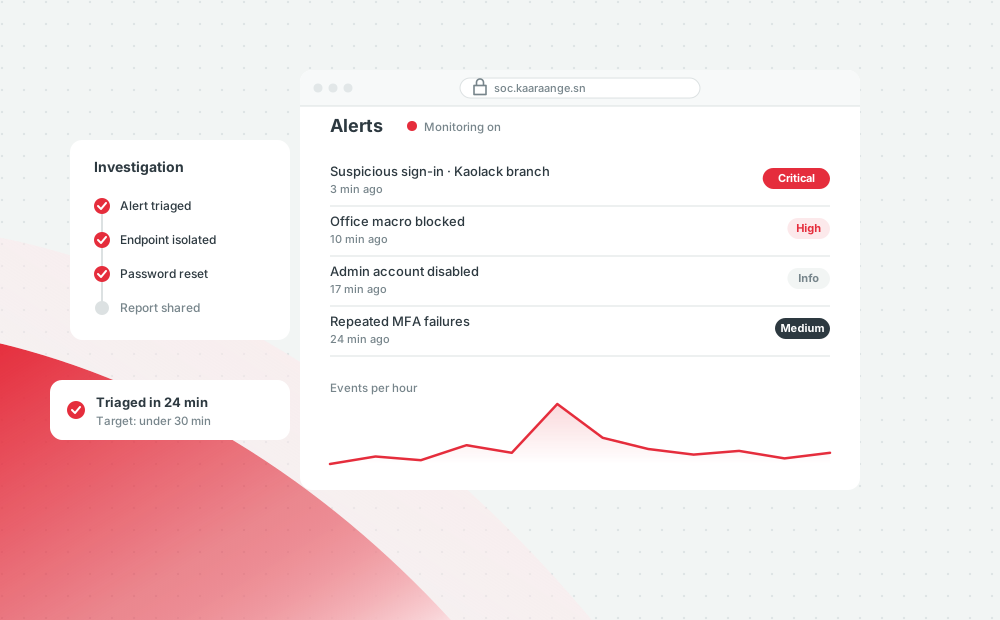
See attacks, react fast and get back to business.
- EDR, SIEM and detection use cases
- Response plan and crisis exercises
- Digital forensics (DFIR)
- Continuity and restore testing
Expertise connected to your challenges.
For leadership teams who want to know where they stand, reduce major risks and prepare their people for an incident.
- Unclear exposure and fuzzy priorities.
- Regulatory or customer requirements to demonstrate.
- No monitoring and no response plan if an incident happens.
We start by understanding usage, constraints and a useful first scope.
What you receive.
Scope and success criteria agreed before work starts.
Assessment and roadmap
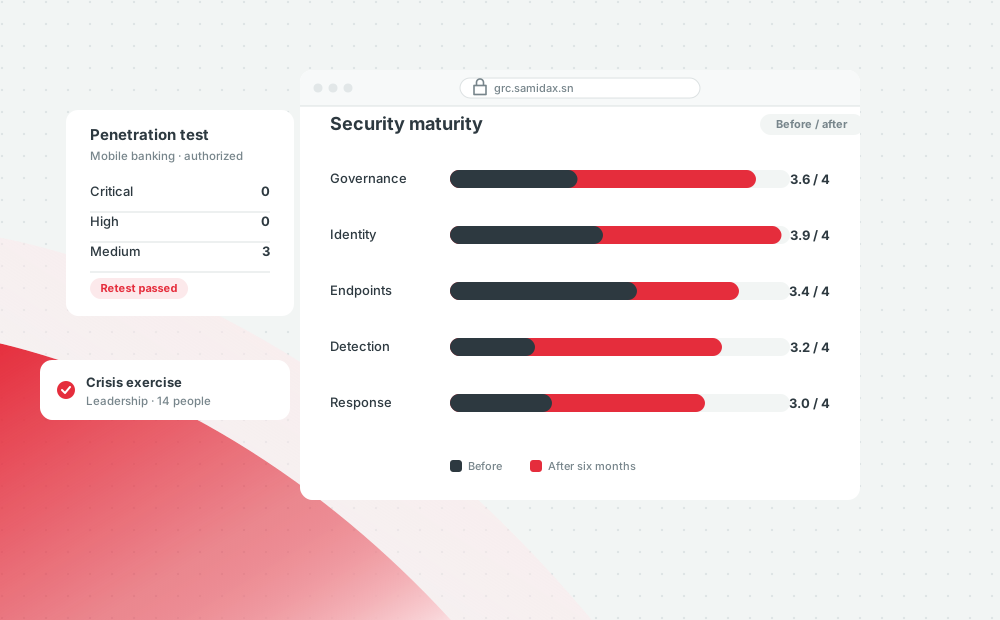
A maturity level, prioritized risks and a plan approved by leadership.
Controls in place
Identity, endpoints, logging and detection configured and documented.
Response capability
A response plan, procedures and a crisis exercise with your teams.
How to get started.
Three engagement types, from the shortest to the longest. Durations are indicative and confirmed after discovery.
Maturity assessment
Current state, risks and a prioritized roadmap.
Penetration test
An authorized scope, rules of engagement and a retest after fixes.
Security program
Roadmap delivery and a fractional CISO.
Technologies
ISO 27001 · NIST CSF · EDR · SIEM · Entra ID · Penetration testing
Selected after discovery, based on your environment and maintenance needs.Before we begin.
Answers to the questions clients ask us most before getting started.
Another question?
Write to us and we will point you to the right expertise and a sensible first step.
Ask a question01Where should we start?
With an assessment. It lets you fix the most serious risks first instead of buying tools at random.
02Do you provide 24/7 monitoring?
Hours, on-call arrangements and response times require a specific agreement. We can also build your internal team’s capability.
Projects in this practice.
From context to results, see how we delivered these projects.
 View the case study
A cybersecurity program to protect 120,000 customer accounts.
Assessment, penetration test, detection and response plan: a microfinance institution’s security brought up to standard in six months.
 View the case study
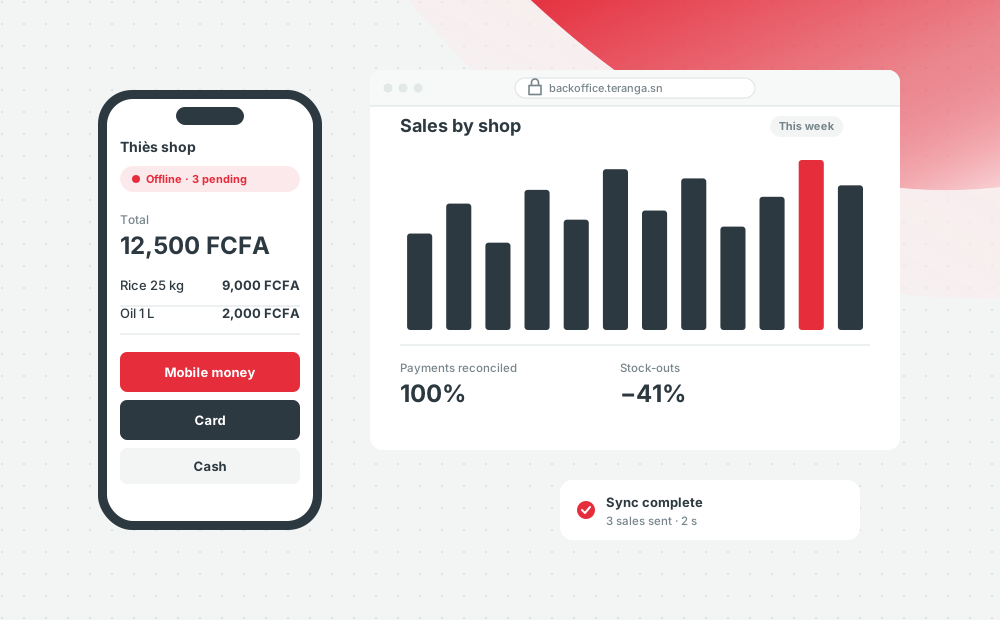
Orders, stock and mobile payments in a single app.
An offline-first app for 38 shops, with mobile money payments reconciled automatically.
Keep exploring.
Our practices work together: a software project is built with cloud and security in mind.
You have the challenge. Let’s make a start.
One conversation is enough to clarify the need and the next useful step.